
Kuvaus
Nahnu Cache Connector for Bunny.net connects your WordPress site to Bunny.net CDN. It syncs cache purges automatically, deploys a full set of production-ready edge rules with one click, and shows live CDN stats directly in your WordPress admin.
For full documentation visit wpbunnyconnector.com.
Automatic cache purge sync
Hooks into your active cache plugin so every purge is mirrored to Bunny CDN in real time. Where possible, per-URL purges are used instead of full zone wipes.
Supported cache plugins (16):
- WP Rocket
- LiteSpeed Cache
- W3 Total Cache
- WP Fastest Cache
- WP Super Cache
- FlyingPress
- Swift Performance
- Hummingbird
- Cache Enabler
- Breeze (Cloudways)
- WP-Optimize
- SpeedyCache
- Super Page Cache (WP Cloudflare Page Cache)
- ZiziCache
- RunCache (Beta)
- SWIS Performance by EWWW Image Optimizer
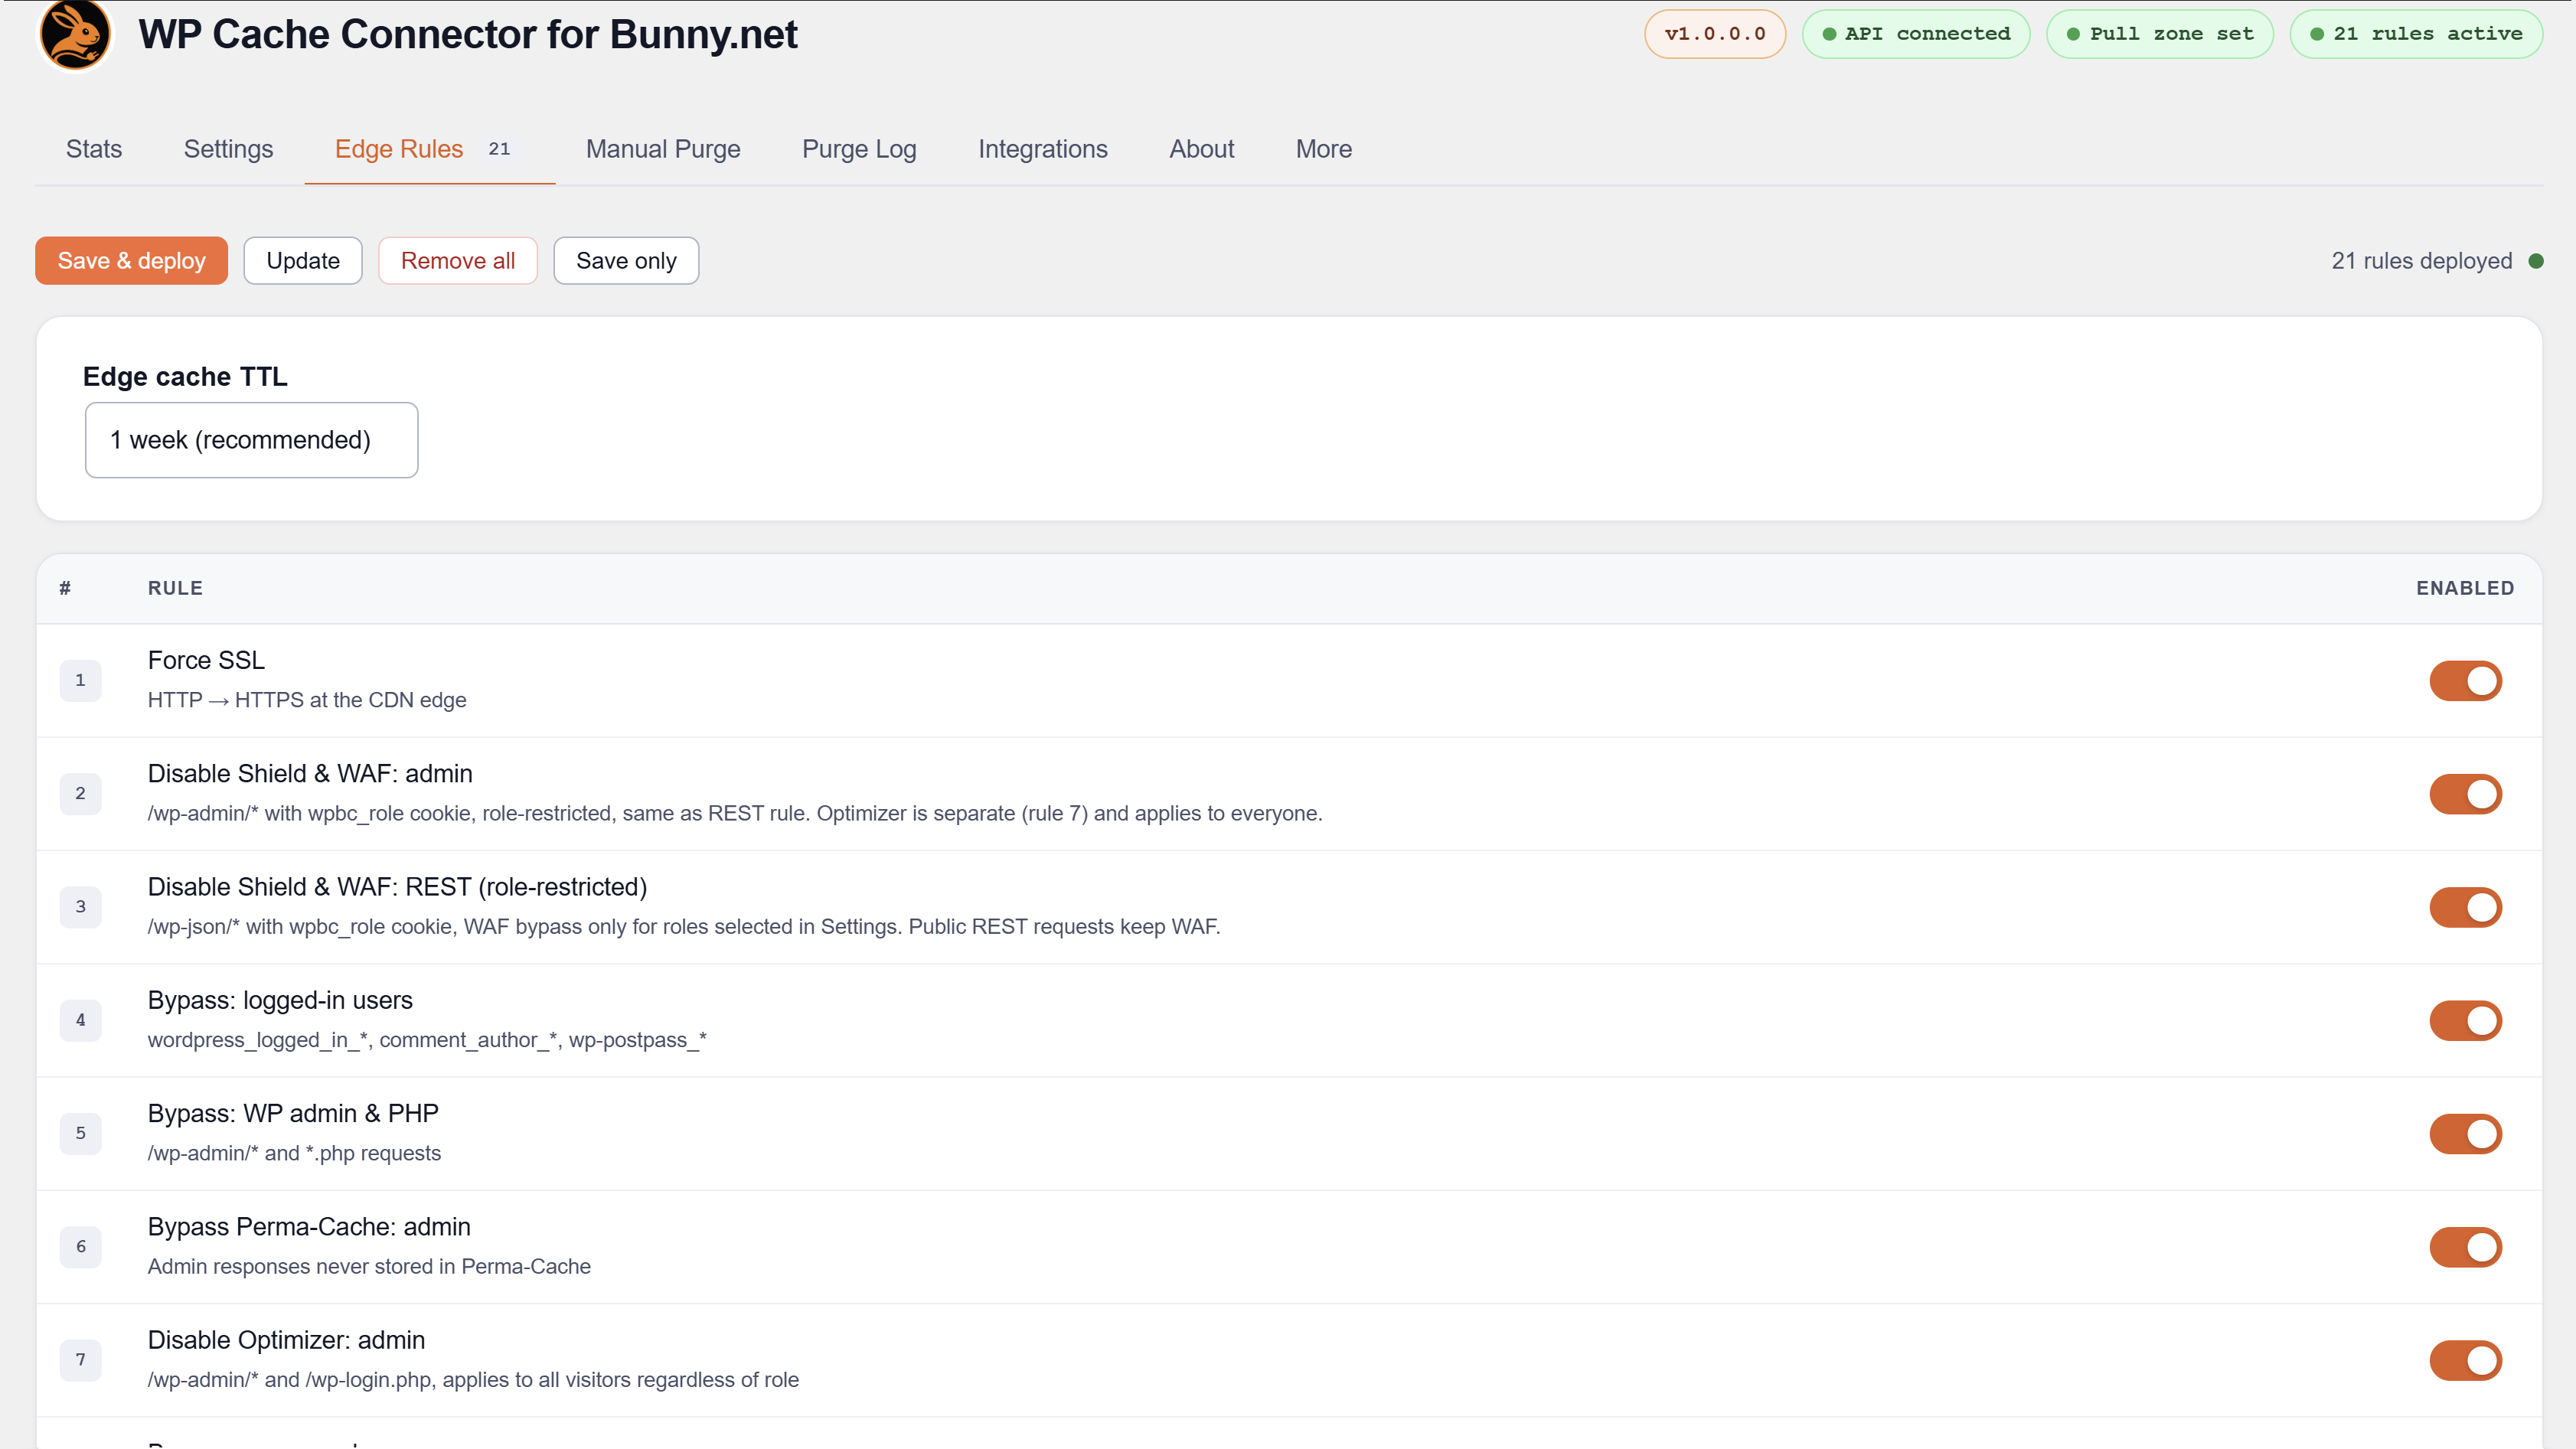
74 edge rules, one-click deploy
Deploys a complete set of rules to your Bunny pull zone covering SSL, admin bypass, WAF bypass, ecommerce cart sessions, membership pages, LMS dashboards, static asset caching, security headers, CORS, and more. Rules are upserted and tracked by GUID — safe to redeploy at any time without duplicates.
Ecommerce bypass
Bypass rules are built automatically from each plugin’s own page settings. No manual URL entry needed.
Supported ecommerce and donation plugins (6):
- WooCommerce
- SureCart
- FluentCart
- Easy Digital Downloads (EDD)
- GiveWP
- WP User Frontend (WPUF)
Membership bypass
Supported membership plugins (13):
- Ultimate Member
- Simple Membership
- Paid Member Subscriptions
- User Registration and Membership
- WP-Members
- WCFM Multivendor Membership
- Restrict Content / Kadence Membership
- ProfilePress
- Indeed Ultimate Membership Pro
- Paid Memberships Pro
- ARMember
- MemberPress
- GiveWP
LMS and community bypass
Supported LMS plugins (9):
- WP User Frontend
- MasterStudy LMS
- Masteriyo LMS
- LearnDash
- Sensei LMS
- Academy LMS
- LifterLMS
- Tutor LMS
- FluentCommunity
Affiliate and community plugins with bypass rules (2):
- FluentAffiliate
- SureDash
Booking and event bypass
Supported booking and event plugins (4):
- Events Manager
- Amelia Booking
- LatePoint
- WP Event Manager
Multilingual support
Bypass rules automatically include translated page URLs when any of these plugins is active:
- WPML
- Polylang
- TranslatePress
Shield WAF — trusted IP whitelist
Disables Bunny Shield WAF inspection for specific IPs or CIDR ranges entered in Settings. Useful for SaaS callbacks, office networks, staging servers, and payment gateway IPs.
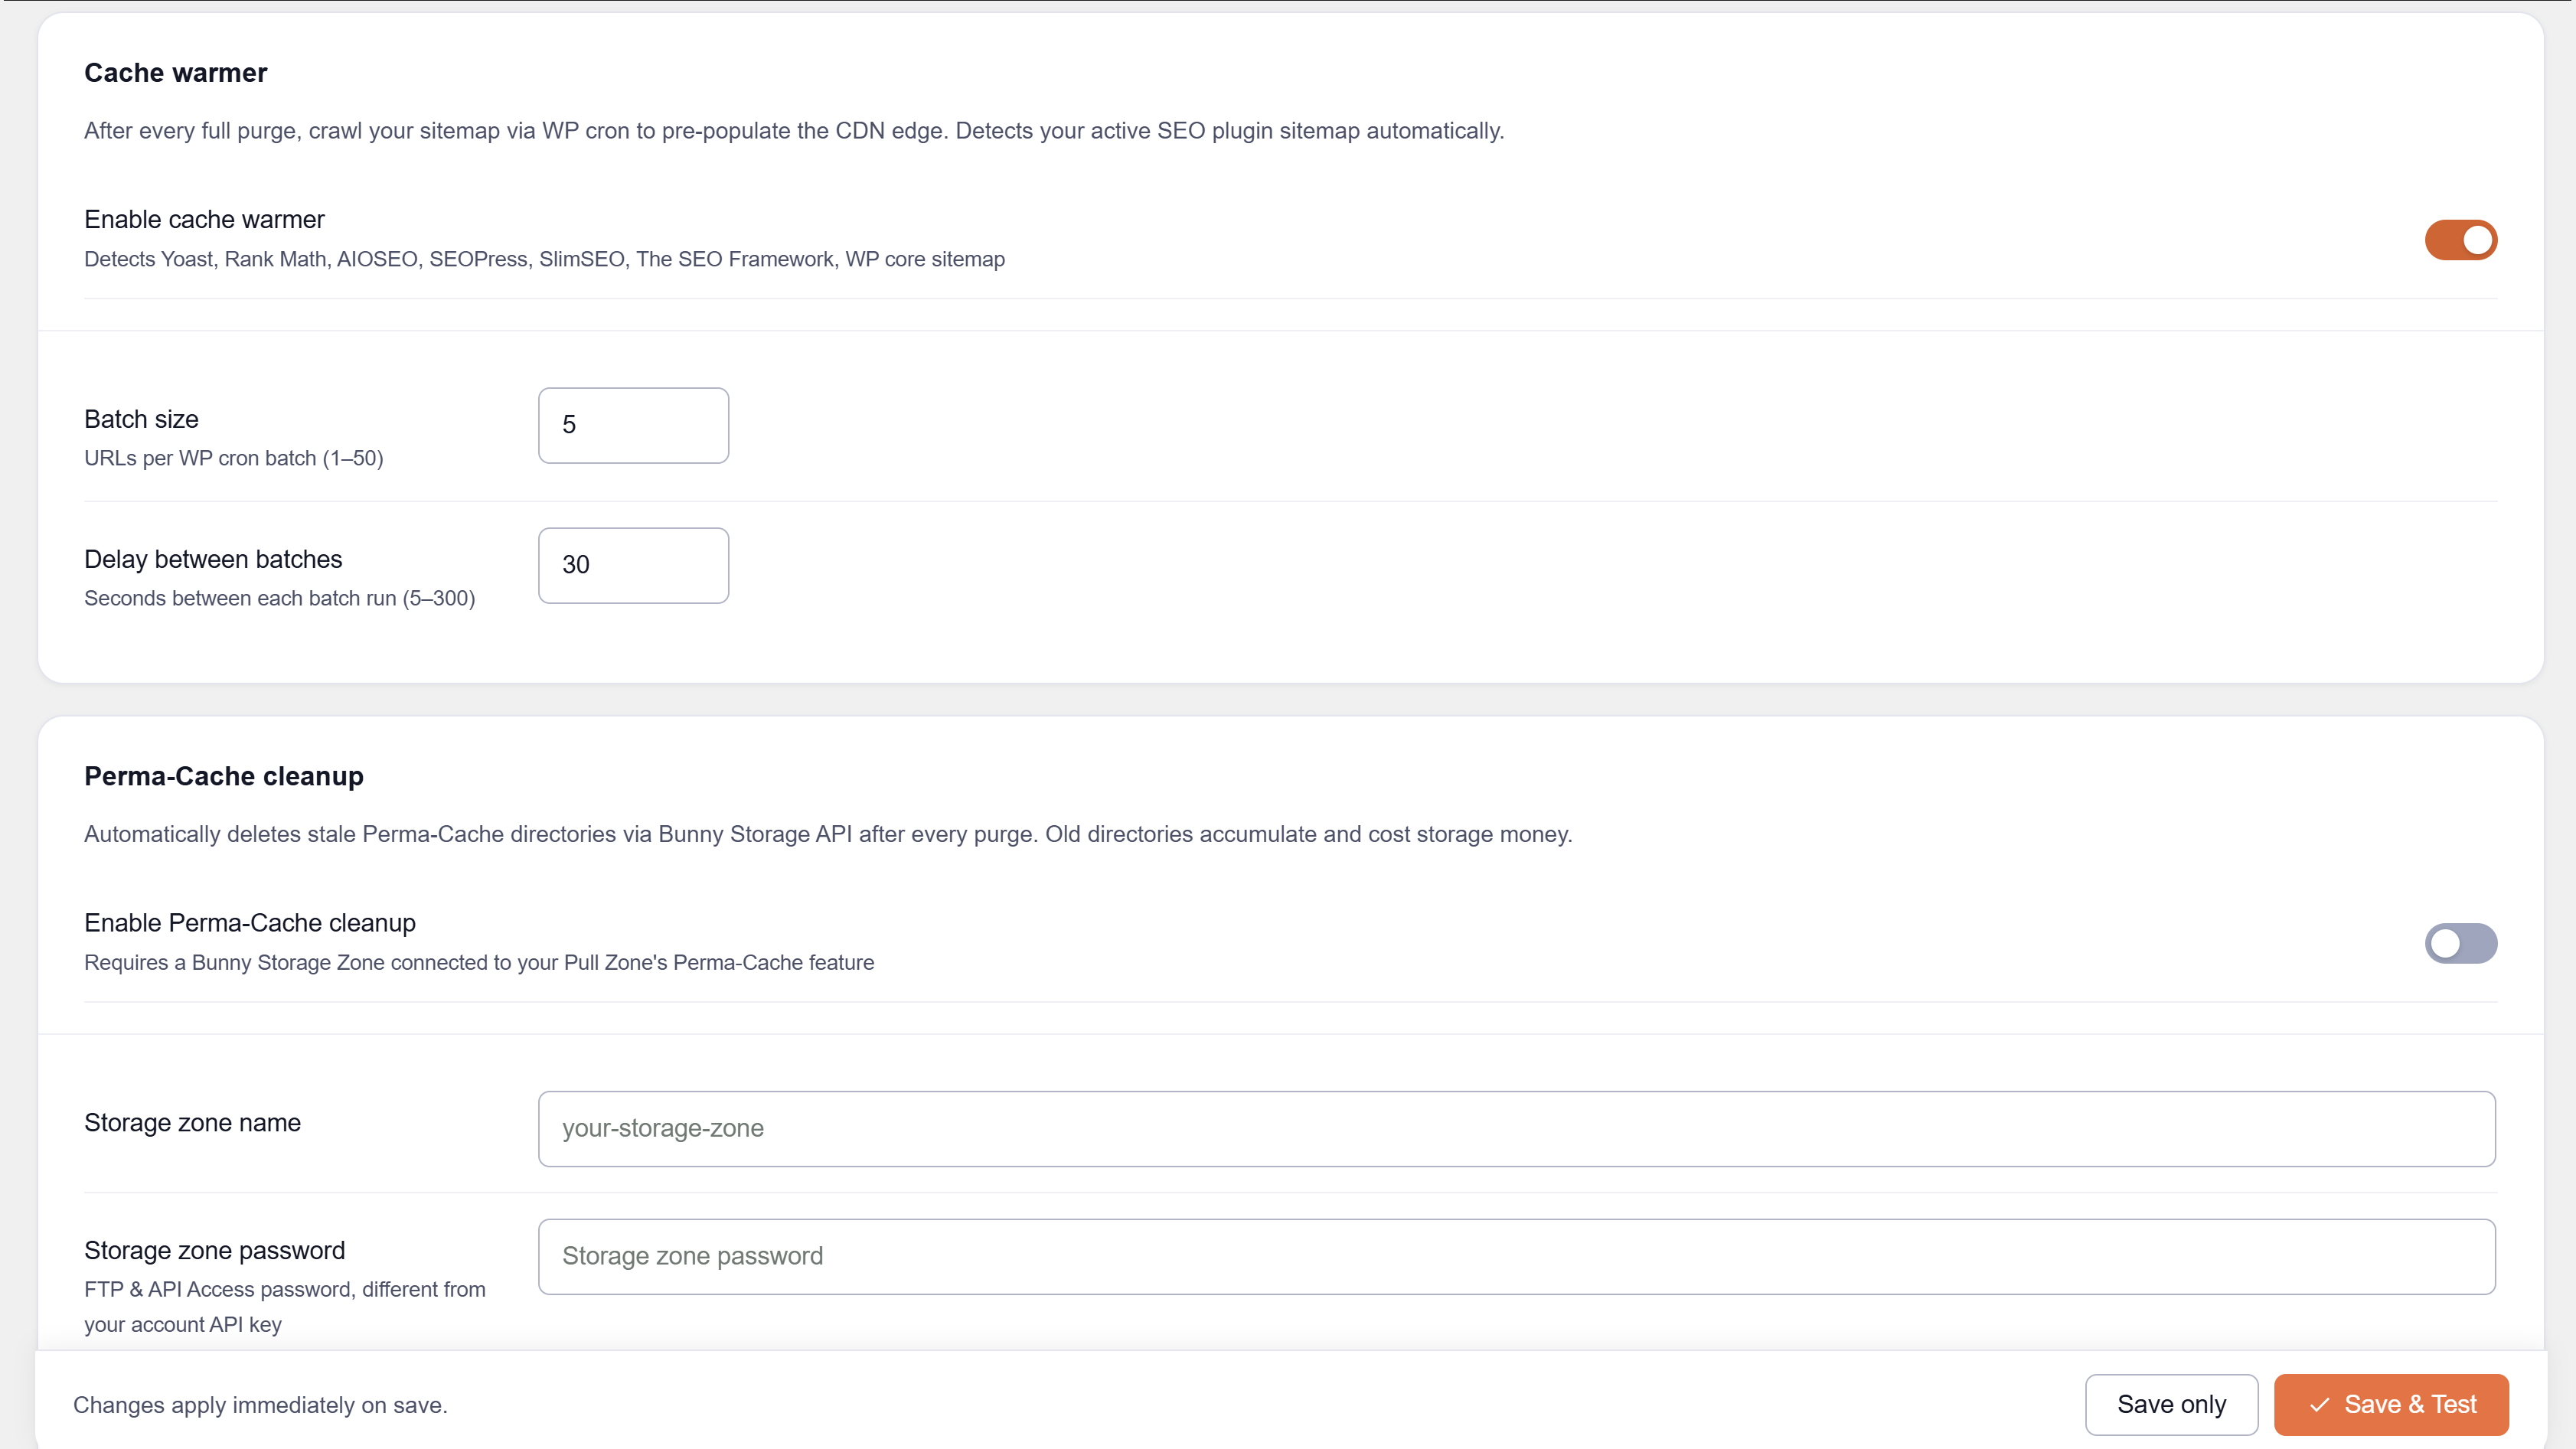
Cache warmer
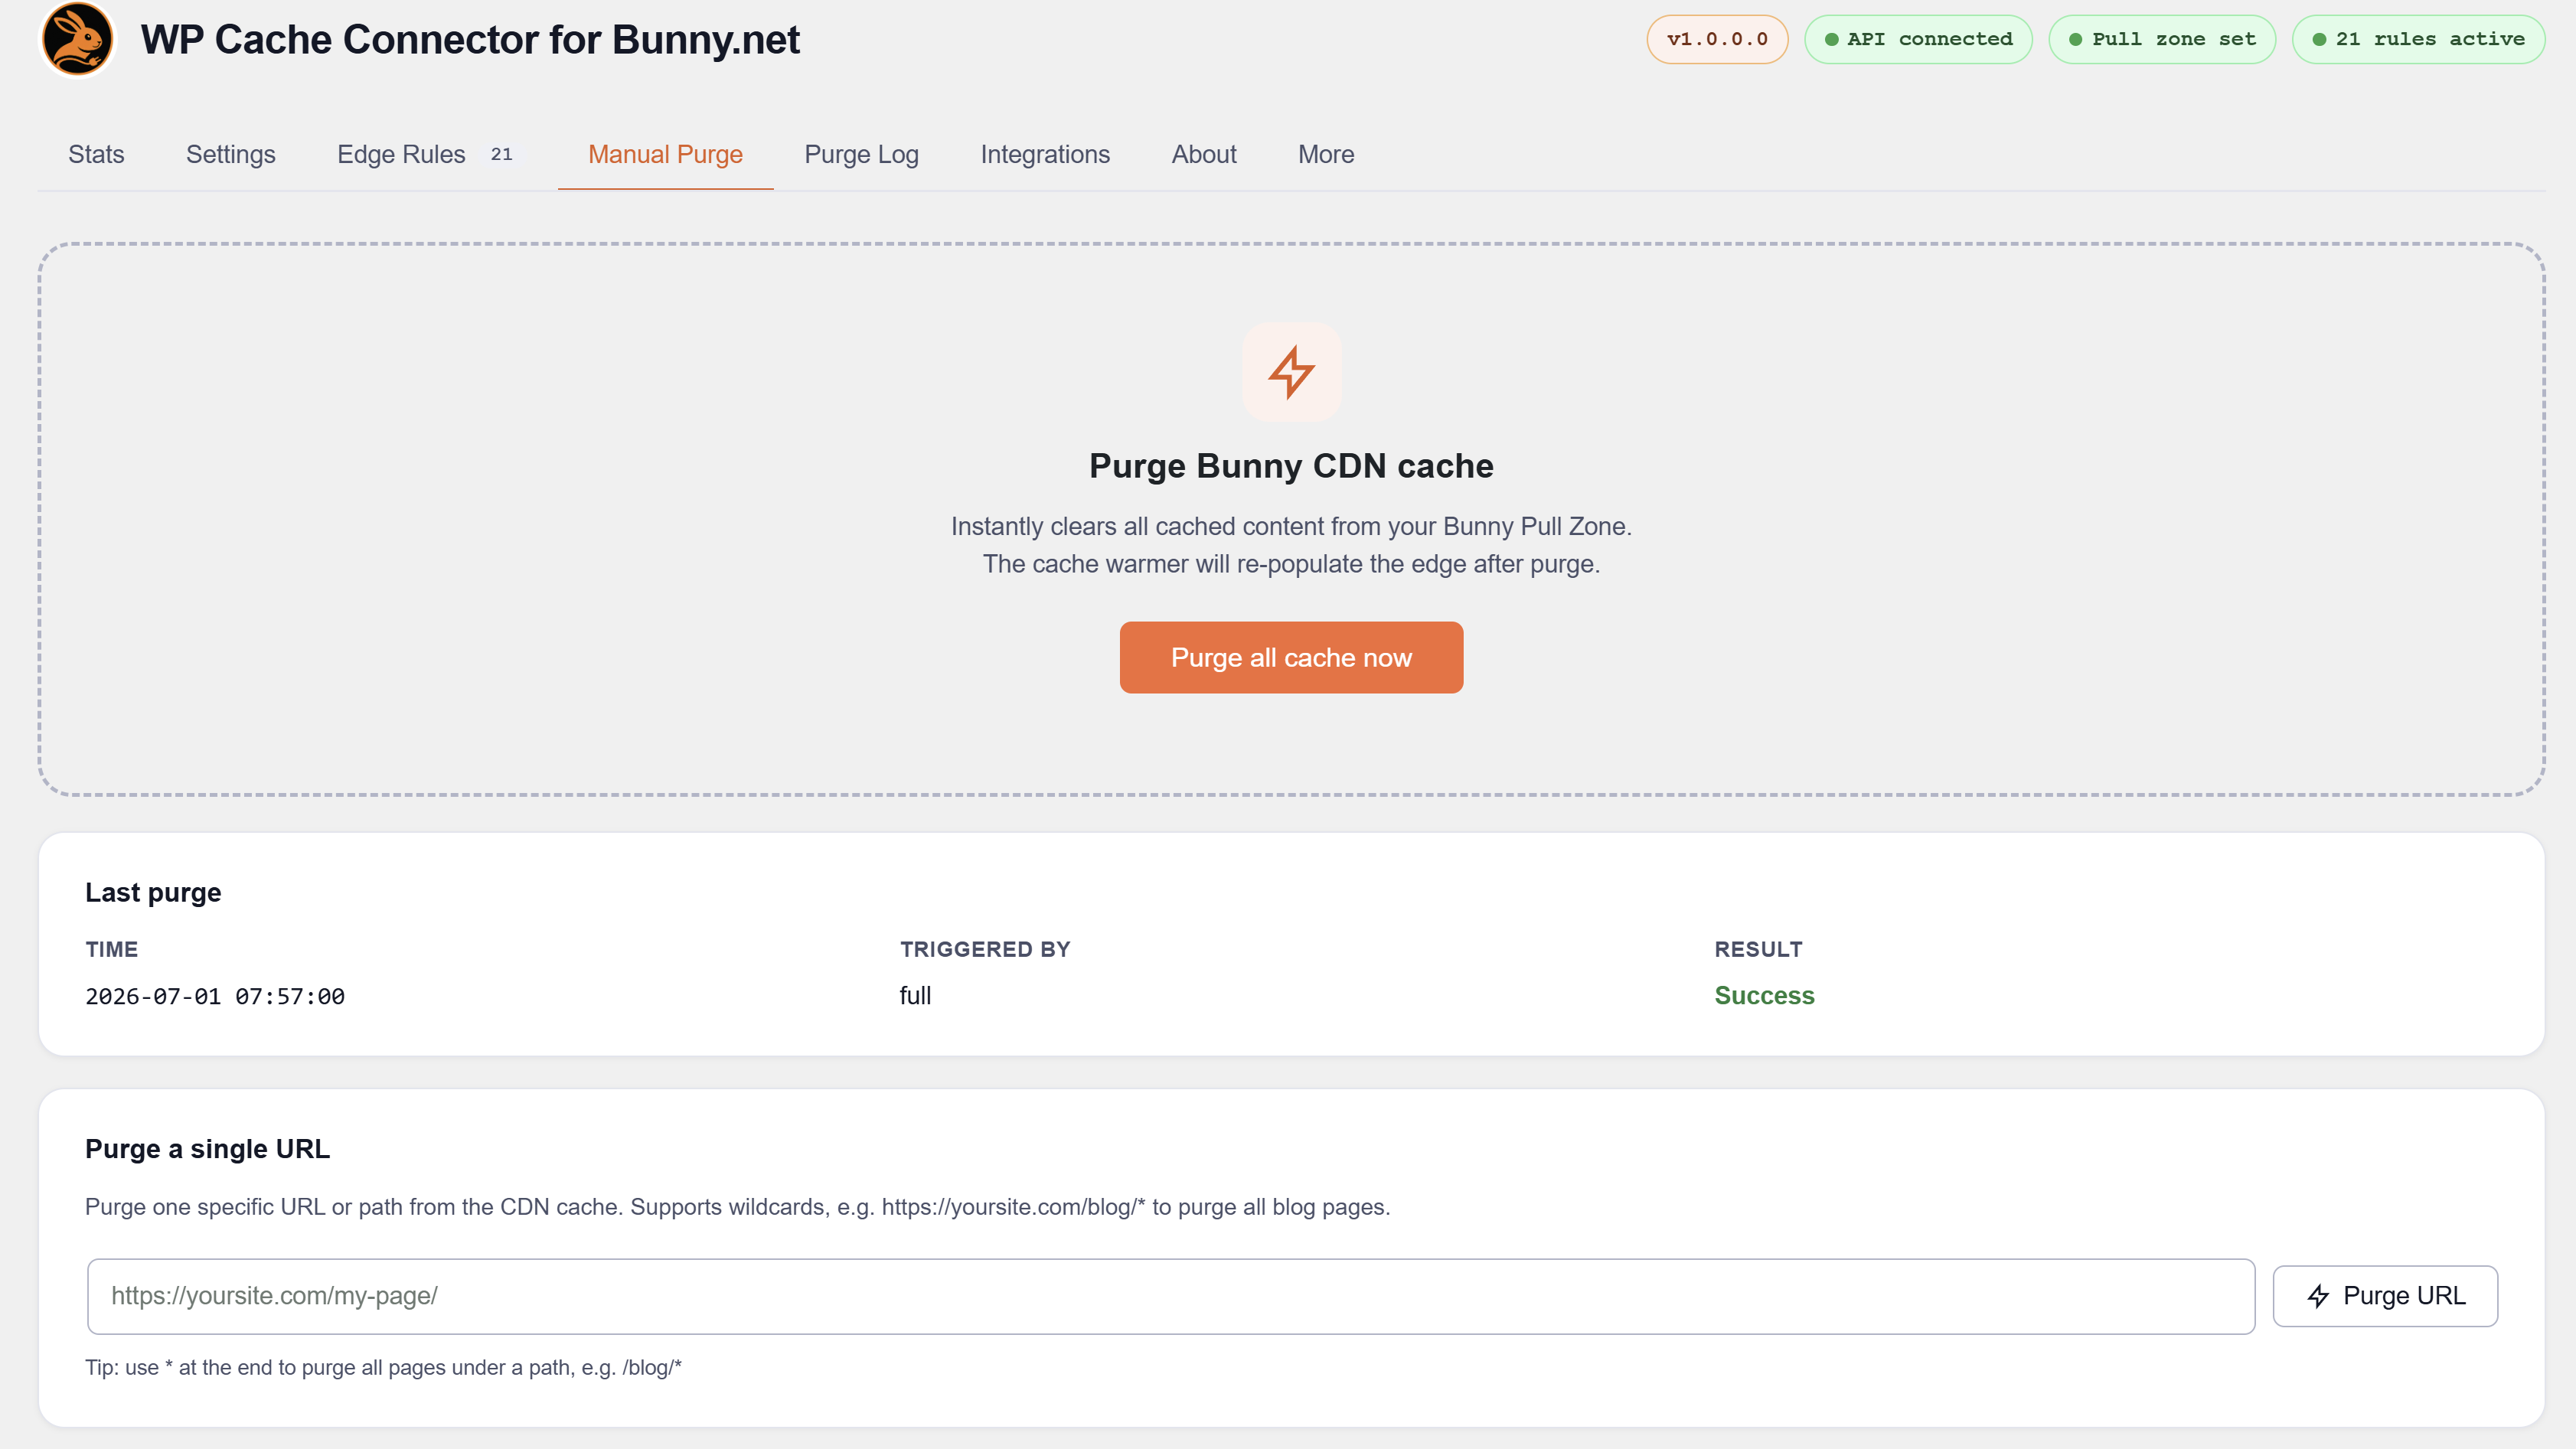
After a full purge, a WP-Cron job crawls your sitemap to pre-warm the CDN edge.
Supported SEO plugins for sitemap auto-detection:
- Yoast SEO
- Rank Math
- All in One SEO
- SEOPress
- SlimSEO
- The SEO Framework
- Squirrly SEO
- WordPress core sitemap (fallback)
Live CDN analytics
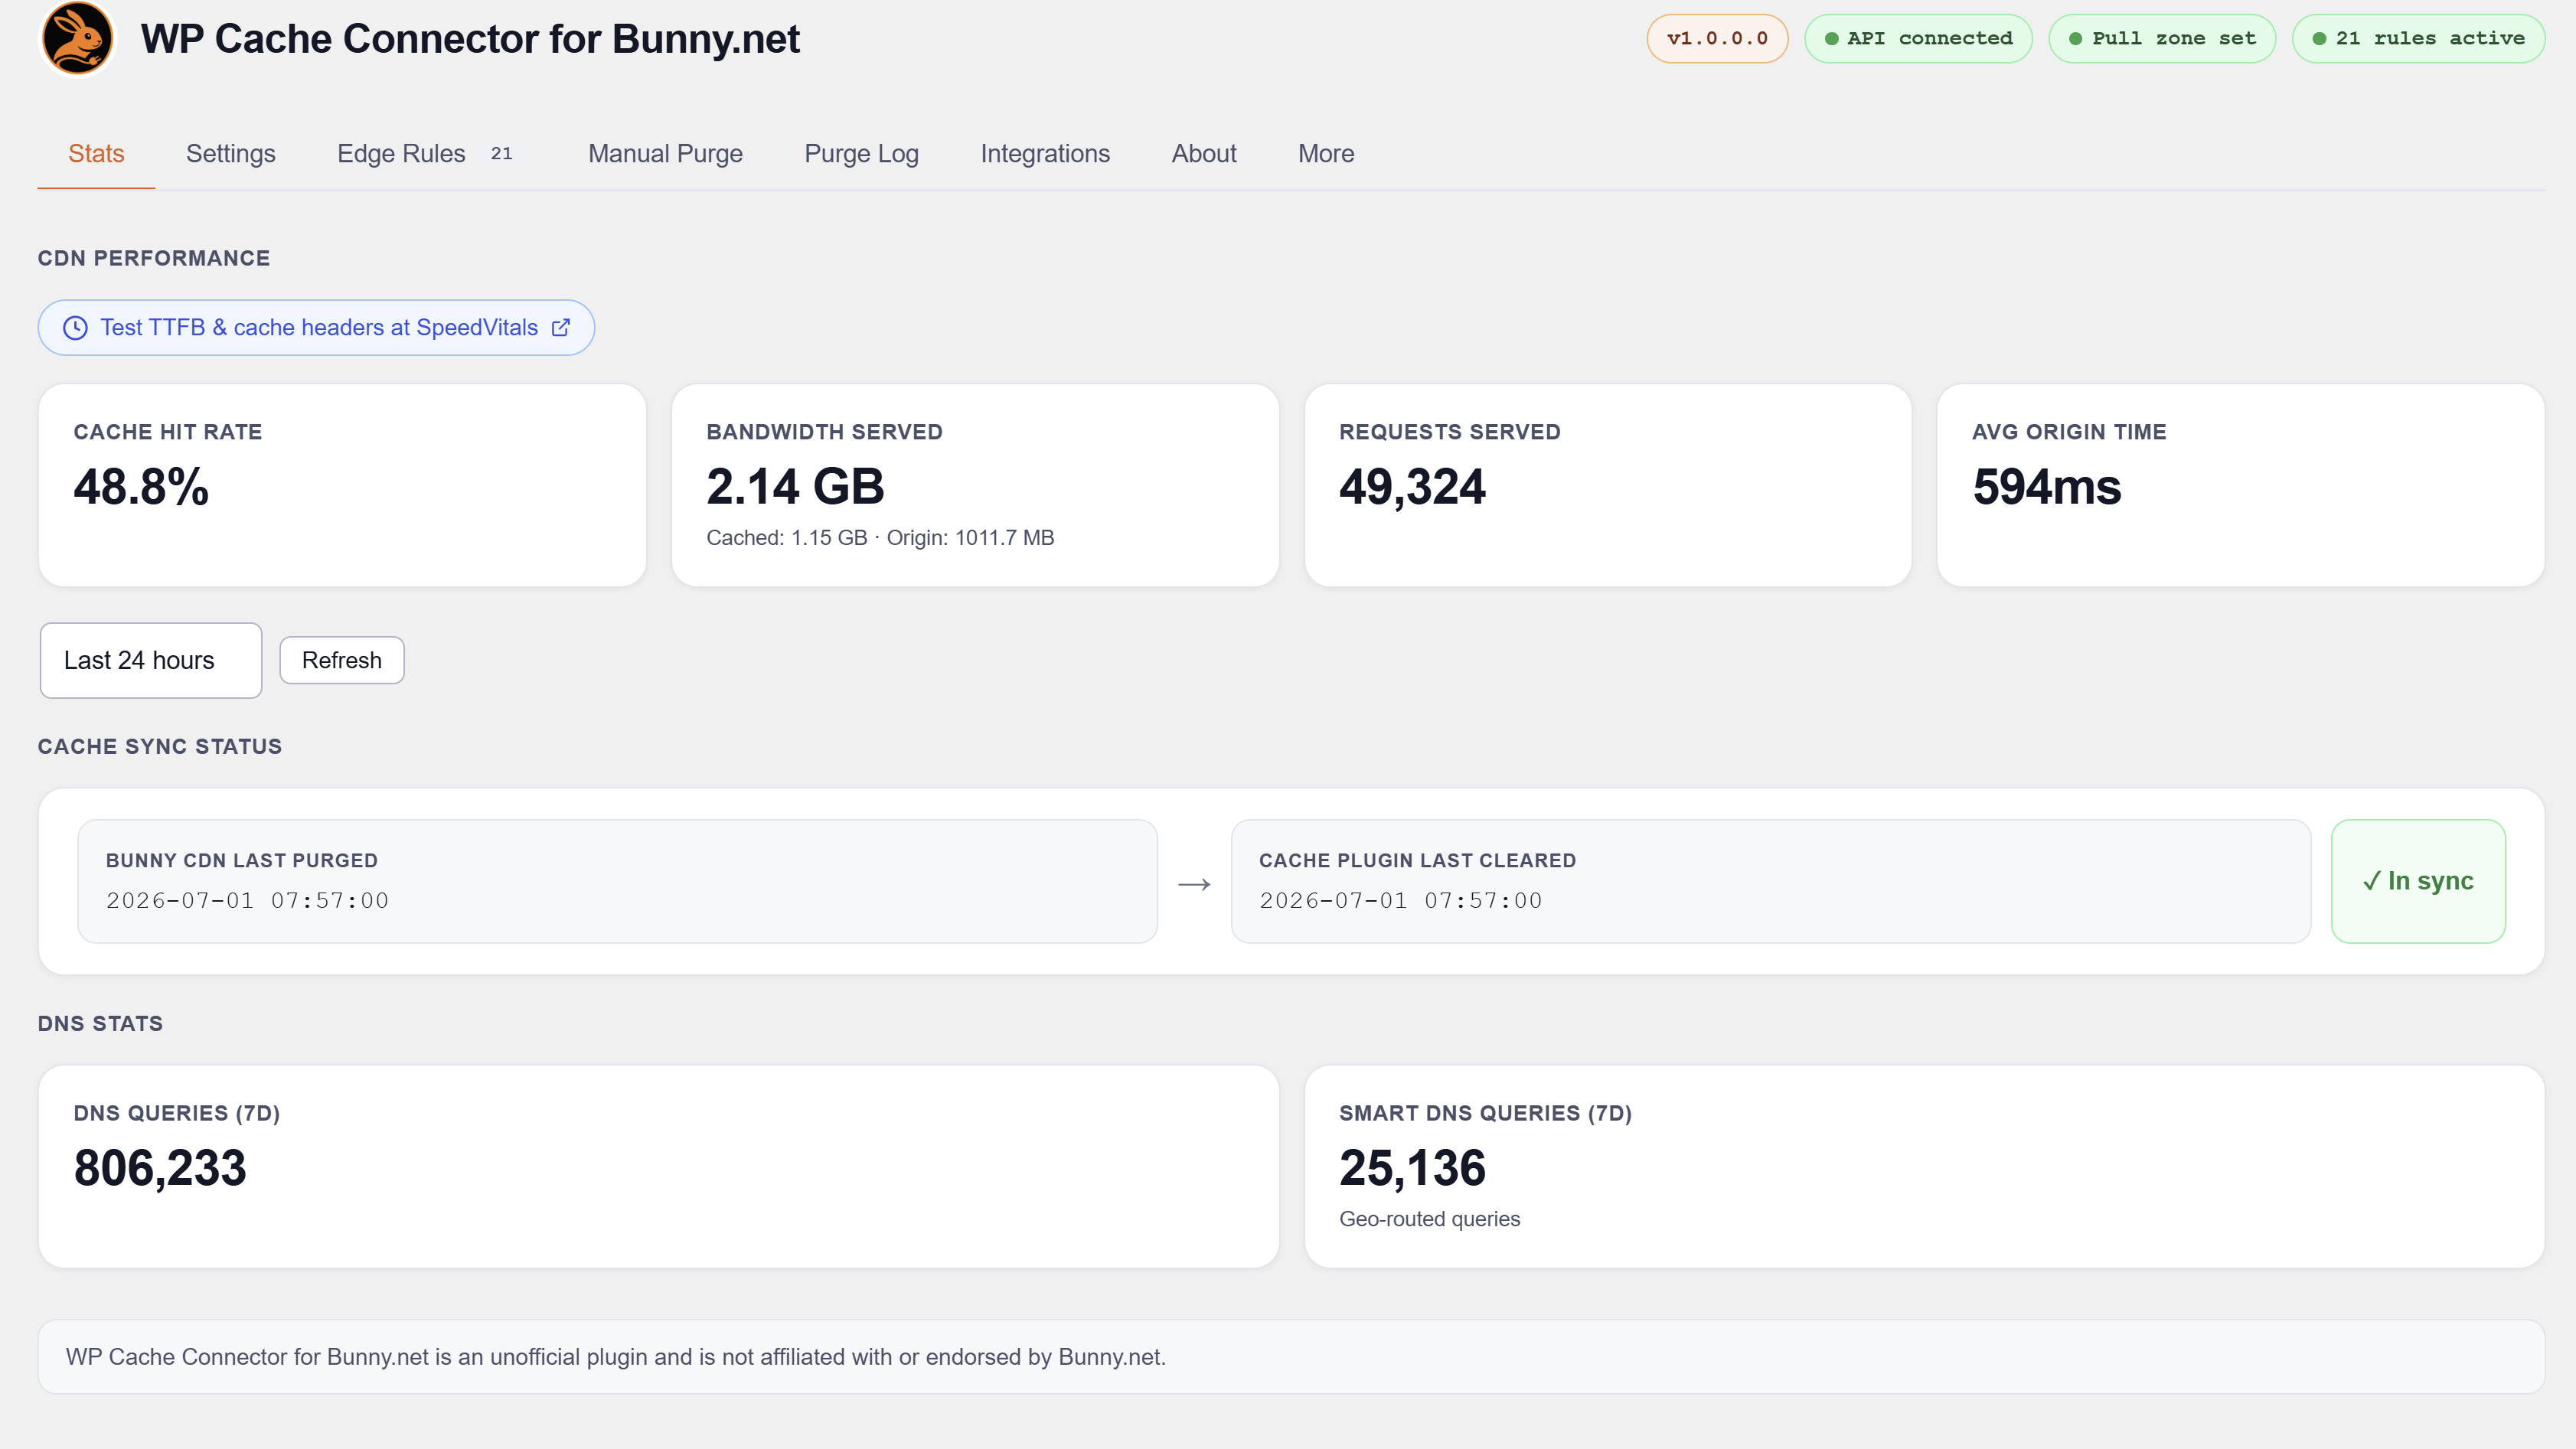
Pull zone stats, DNS stats, bandwidth breakdown, cache hit rate, and cache sync status — all inside WordPress admin.
Perma-Cache cleanup
Deletes stale Perma-Cache files from Bunny Storage immediately after a full purge, without waiting for TTL expiry.
Checked, no integration needed
These plugins were analysed and confirmed fully compatible with no bypass rules required:
- Wordfence, All-In-One Security, Jetpack, Solid Security, Security by CleanTalk
- Complianz GDPR, CookieYes
- SureMembers, WishList Member, Members (by MemberPress)
- bbPress, Fluent Boards
- The Events Calendar, FluentBooking
- Autoptimize, FlyWP, Redis Object Cache, Aruba HiSpeed Cache, Comet Cache, SiteGround Speed Optimizer, EWWW Image Optimizer
For the full compatibility list and documentation visit wpbunnyconnector.com.
Developer hooks and filters
Third-party plugins can integrate with Nahnu Cache Connector for Bunny.net without any changes to this plugin. Four filters are available.
wpbc_shield_bypass_ips — add trusted IP addresses or CIDR ranges to the Bunny Shield WAF bypass list. Merged with IPs entered manually in Settings and deployed as part of rule 74.
wpbc_shield_bypass_urls — disable Bunny Shield WAF inspection on specific URL path patterns. Deploys as rule 75 when any plugin uses this filter.
wpbc_cache_bypass_urls — add URL path patterns to the Bunny CDN cache bypass list. Deploys as rule 76 when any plugin uses this filter.
wpbc_compatible_plugins — register a plugin in the Integrations tab with a name, company, and compatibility note.
For full developer documentation and code examples visit wpbunnyconnector.com.
External services
This plugin communicates with the Bunny.net API (api.bunny.net) to purge cache, manage edge rules, and retrieve statistics. An active Bunny.net account and API key are required. No visitor data is transmitted. See Bunny.net Privacy Policy (https://bunny.net/privacy) and Terms of Service (https://bunny.net/tos).
Disclaimer
This is an independent third-party tool. It is not affiliated with, endorsed by, or sponsored by Bunny.net.
Privacy Policy
Nahnu Cache Connector for Bunny.net does not collect or transmit any data about your site’s visitors. No analytics, no tracking, no third-party data sharing.
The plugin communicates with the Bunny.net API to purge cache, fetch statistics, and manage edge rules. Data sent is limited to your Bunny API key (in request headers), pull zone ID, and URLs to purge. See Bunny.net’s Privacy Policy for details on how Bunny.net handles this data.
No data is sent to Nahnu Plugins or any third party other than Bunny.net.
Kuvankaappaukset

Asennus
- Upload the
nahnu-cache-connector-bunny-netfolder to/wp-content/plugins/, or install via Plugins > Add New > Upload. - Activate the plugin through the Plugins menu.
- Go to Settings > Bunny Connector.
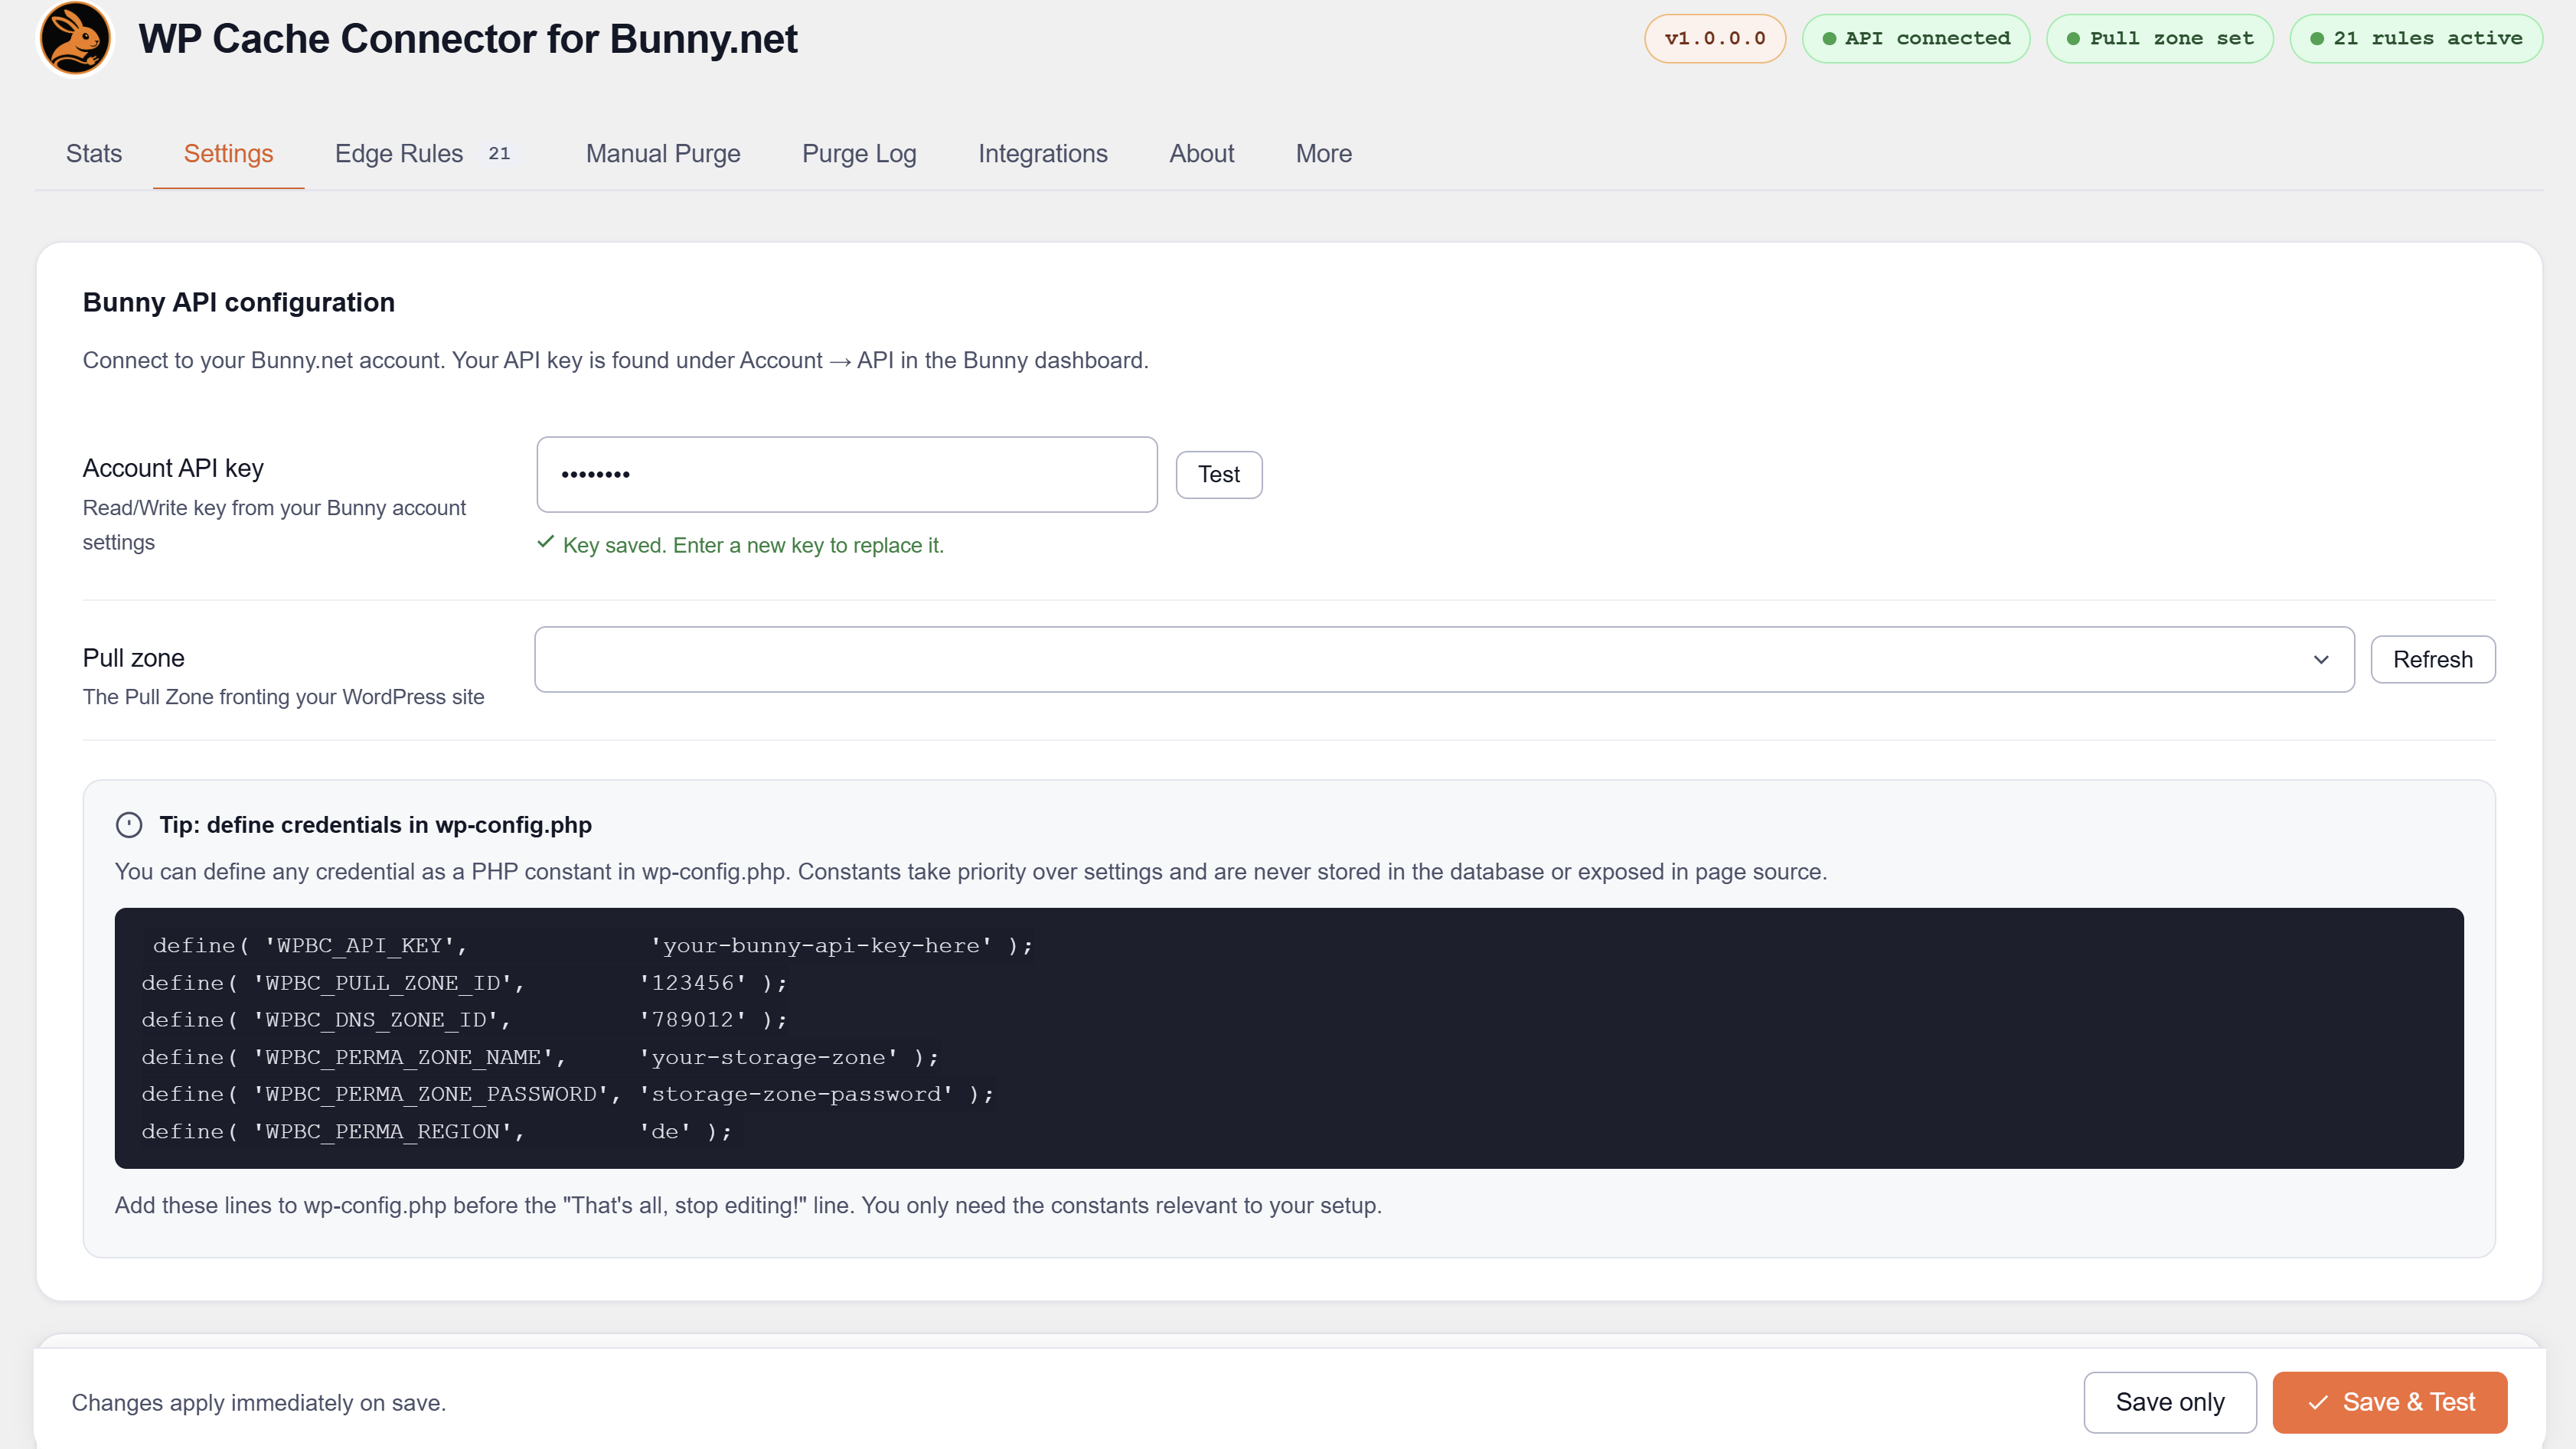
- Enter your Bunny.net Account API Key and click Test to verify it.
- Select your pull zone from the searchable dropdown.
- Click Save & deploy in the Edge Rules tab to deploy all rules to your pull zone.
Your API key is the Account API Key found in the Bunny.net dashboard under Account > API, not a pull zone access key.
For full setup instructions visit wpbunnyconnector.com.
Defining constants (optional)
Lock any value in wp-config.php to prevent it being stored in or changed via the database. When a constant is defined, the corresponding field is hidden in the UI.
define( 'WPBC_API_KEY',             'your-bunny-api-key' );
define( 'WPBC_PULL_ZONE_ID',        '123456' );
define( 'WPBC_DNS_ZONE_ID',         '789012' );
define( 'WPBC_PERMA_ZONE_NAME',     'your-storage-zone' );
define( 'WPBC_PERMA_ZONE_PASSWORD', 'storage-zone-password' );
define( 'WPBC_PERMA_REGION',        'de' );
Available values for WPBC_PERMA_REGION: de (Falkenstein), uk (London), ny (New York), la (Los Angeles), sg (Singapore), se (Stockholm), br (Sao Paulo), syd (Sydney), jh (Johannesburg).
UKK
-
Does this work with any cache plugin?
-
It integrates with 16 specific cache plugins listed above. On sites not using any of them, you can still use the edge rules, manual purge, admin bar button, and CDN stats — purges just need to be triggered manually or via the post save / plugin update triggers rather than automatically mirroring a cache plugin’s hooks.
-
Do the ecommerce, membership, and LMS bypass rules deploy automatically?
-
Yes. Each bypass rule checks for its plugin at deploy time using
class_exists()ordefined(). If WooCommerce is not active, the WooCommerce rules are skipped. If MasterStudy LMS is active, its rules are deployed. No manual configuration needed. -
Does it work with WPML, Polylang, or TranslatePress?
-
Yes. Bypass rules for ecommerce and membership plugins automatically include translated page URLs when any of these plugins is active.
-
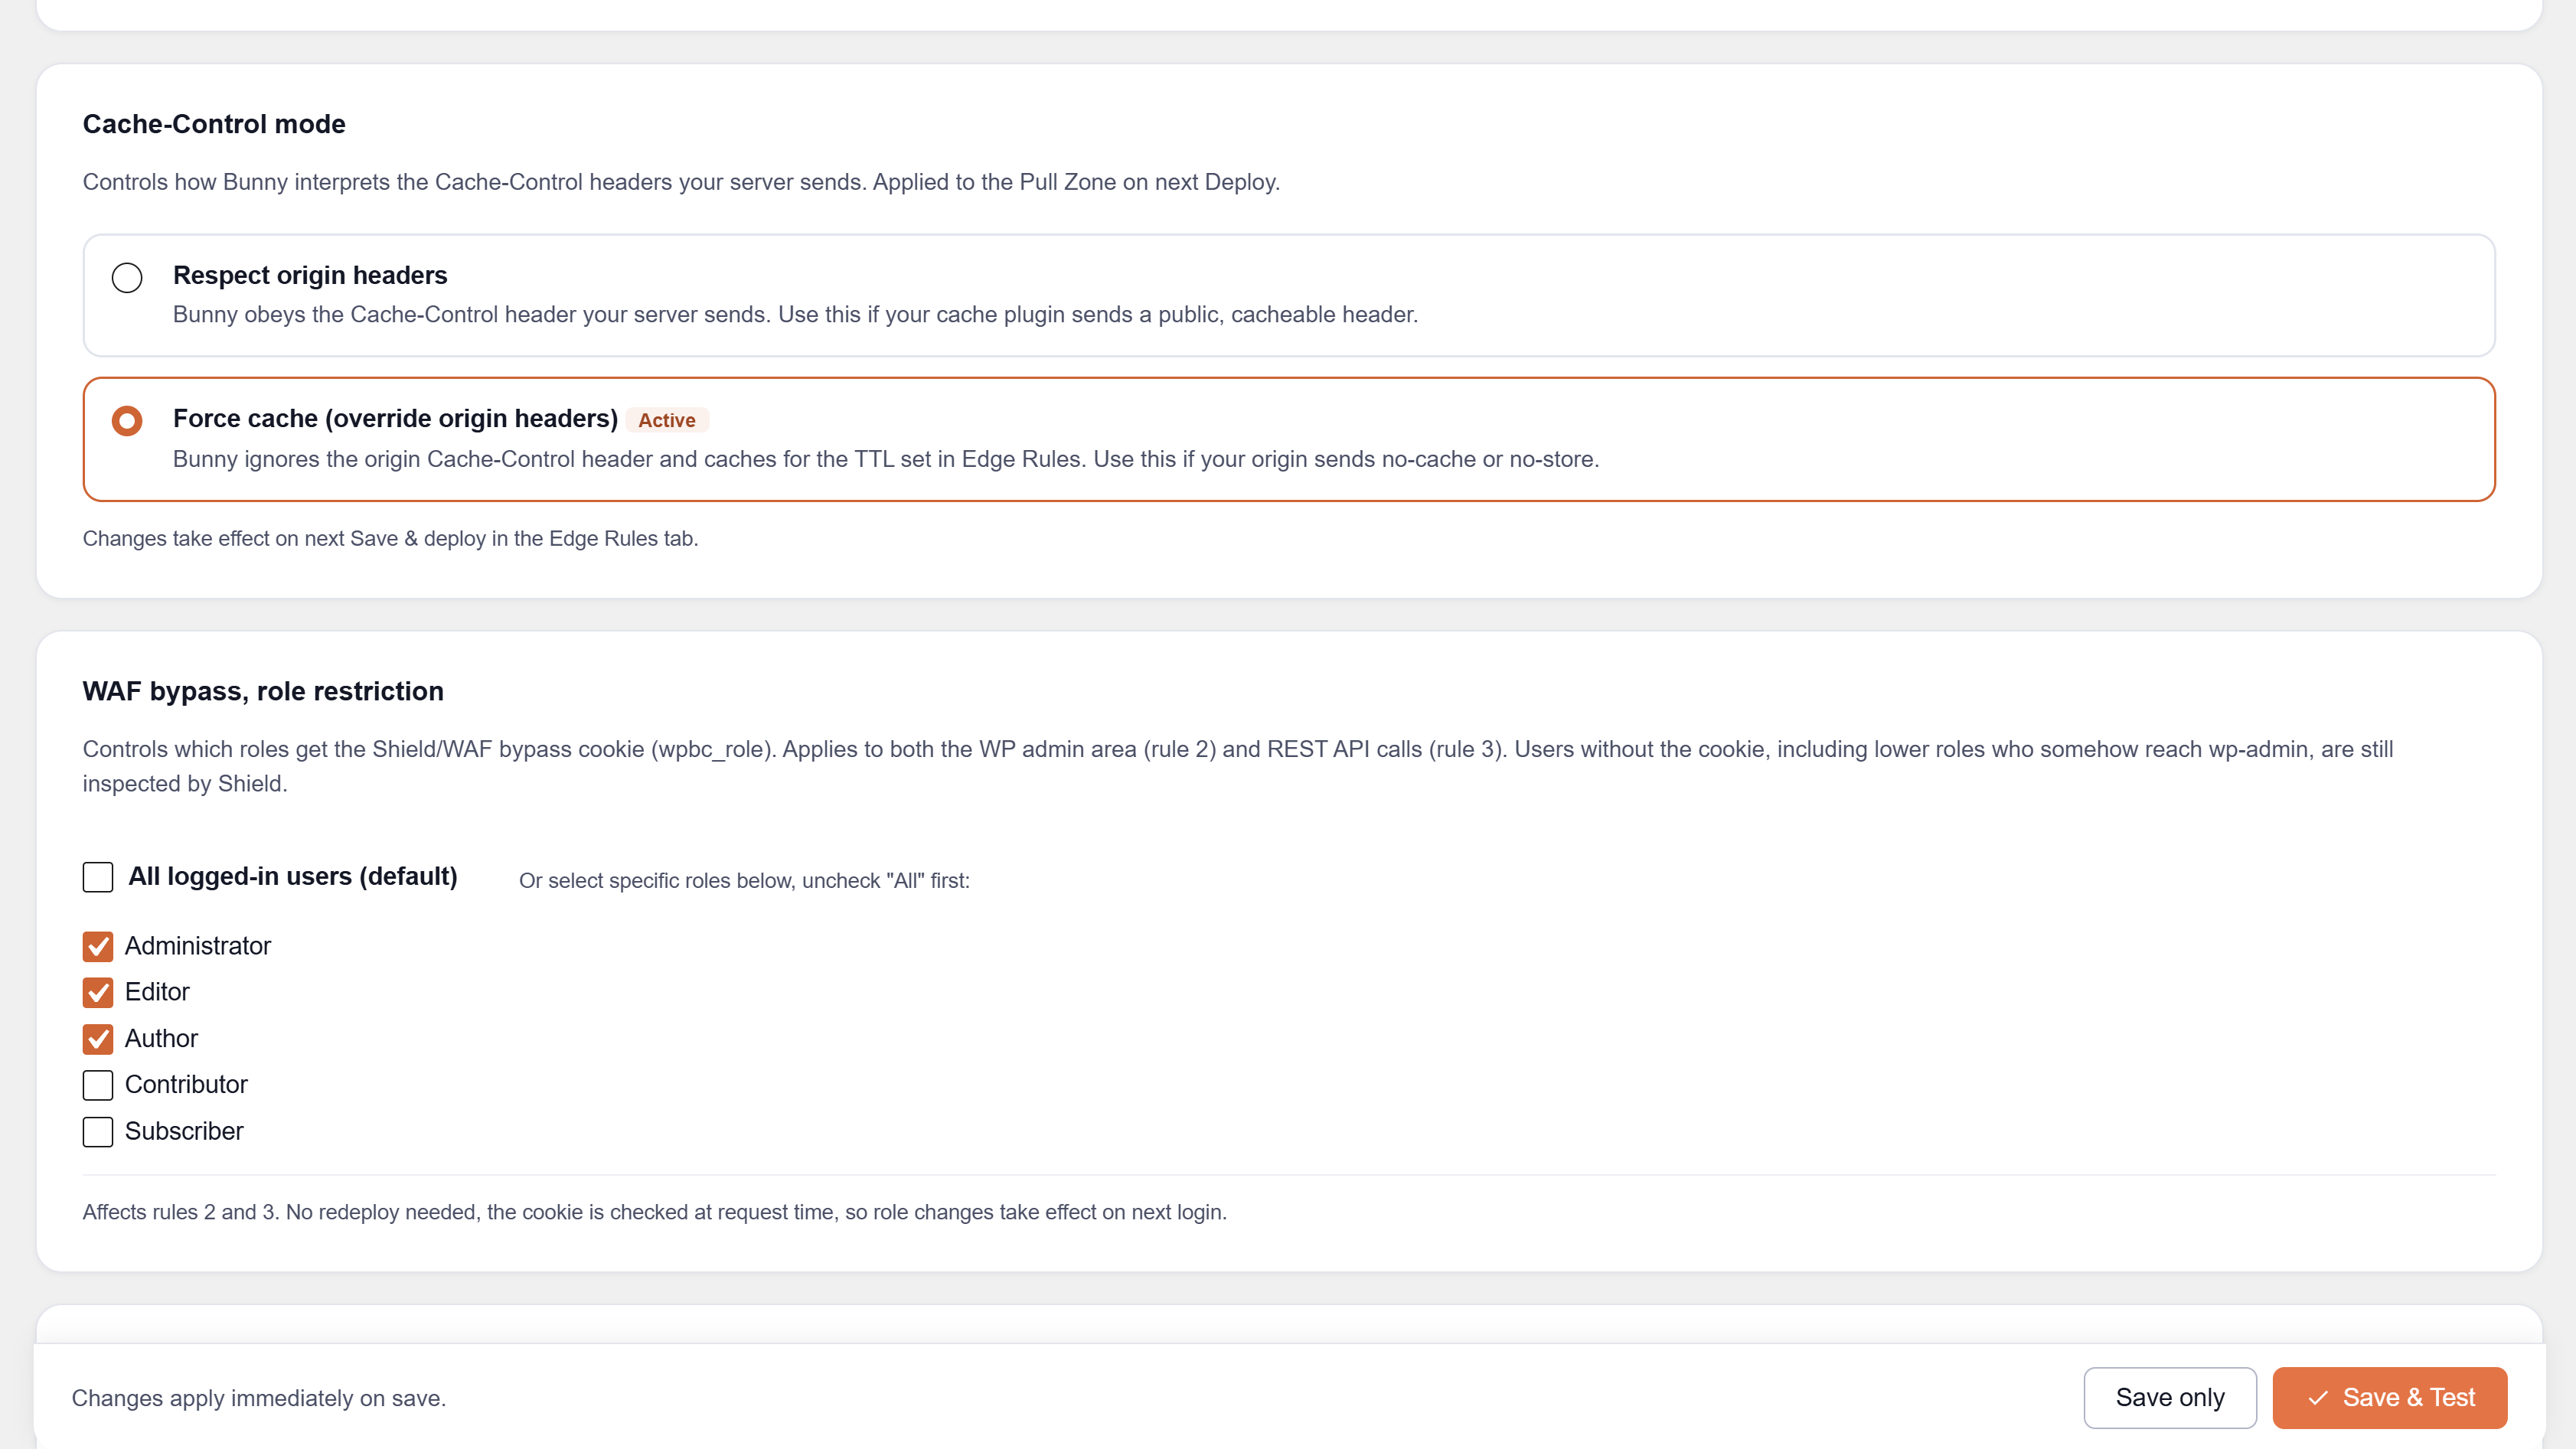
What is Force Cache mode?
-
Some cache plugins send
Cache-Control: max-age=0to Bunny, which tells Bunny not to cache. Force Cache mode overridesCacheControlMaxAgeOverrideon your pull zone so Bunny caches HTML for the configured TTL regardless of what the origin sends. -
Can I use this with Bunny Perma-Cache?
-
Yes. Enable Perma-Cache cleanup in Settings and provide your Bunny Storage zone credentials. After every full purge the plugin lists and deletes stale Perma-Cache files so visitors always get fresh content.
-
Where do I find my Bunny API key?
-
In the Bunny.net dashboard, go to Account > API. Use the Account API Key — not a pull zone access key. The account key is required to manage edge rules and list pull zones.
-
Why do some rules in the deploy results show (1/6) or (2/6) in the name?
-
Bunny’s API limits each rule trigger to 5 URL patterns. Rules that cover many file extensions are automatically split into batches of 5, and each batch becomes a separate rule. The suffix shows which batch you are looking at.
-
Why is the physical rule count in Bunny higher than 74?
-
Batched rules each occupy multiple slots. On a site with www and non-www hostnames and all integrations active, the physical count will exceed 74. The plugin tracks all rule GUIDs and cleans up stale batches automatically when you redeploy.
-
Why are LMS course and lesson pages not in the bypass rules?
-
Most LMS plugins register course and lesson content as public custom post types with standard cacheable URLs. Only per-user pages (student dashboards, checkout, registration, account) need a bypass rule. The plugin makes this distinction based on each plugin’s source code.
-
Yes. The
wpbc_rolecookie is set on theset_auth_cookieaction, which fires for all login methods including MainWP, SSO plugins, and magic link plugins. -
Is this compatible with security plugins like Wordfence or AIOS?
-
Yes. Security plugins operate at the request or firewall layer and are fully compatible. See the Integrations tab for the complete list.
-
Will NitroPack work alongside this plugin?
-
Not as a CDN. NitroPack operates its own cloud CDN layer. Running both NitroPack CDN and Bunny CDN as proxy simultaneously creates a double-CDN conflict.
-
Can my plugin integrate with Nahnu Cache Connector for Bunny.net?
-
Yes. Four PHP filters are available so any plugin can integrate without changes to this plugin:
wpbc_shield_bypass_ips -- add trusted IPs or CIDR ranges to the WAF bypass list.
wpbc_shield_bypass_urls -- disable Shield WAF on specific URL paths.
wpbc_cache_bypass_urls -- add URL paths to the CDN cache bypass list.
wpbc_compatible_plugins -- register in the Integrations tab.
See full developer documentation at wpbunnyconnector.com.
-
My plugin is not listed — can you add it?
-
Yes. Visit wpbunnyconnector.com/support to request a plugin check.
-
How is the API key stored? Is it secure?
-
The API key is stored in the WordPress options table. It is never output in HTML, never sent to the browser in JavaScript, and never included in any AJAX response. It is sent only in HTTP request headers to the Bunny.net API. All admin AJAX endpoints require a valid nonce and
manage_optionscapability.
Arvostelut
There are no reviews for this plugin.
Avustajat & Kehittäjät
“Nahnu Cache Connector for Bunny.net” perustuu avoimeen lähdekoodiin. Seuraavat henkilöt ovat osallistuneet tämän lisäosan kehittämiseen.
Avustajat
Käännä “Nahnu Cache Connector for Bunny.net” omalle kielellesi.
Oletko kiinnostunut kehitystyöstä?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Muutosloki
1.0.9
- Fixed: Fatal error on the settings page (”Undefined array key context” / str_replace() TypeError). Automatic edge rule deploys wrote Purge Log entries in a different shape, and the Purge Log tab crashed on them. The page stopped partway, before its script was printed, so no data loaded and the tabs did nothing. Since 1.0.5 automatic deploys run on every update, so most sites with a recent update were affected.
- Fixed: All Purge Log entries are now written in one format, and older entries already stored on your site are read correctly. Malformed entries are skipped instead of breaking the page.
- Fixed: The Purge button, WP-CLI (wp bunny purge) and the REST purge endpoint judged success by the newest log entry, which could belong to another event. They now use the purge result itself.
- Fixed: wpbc_status and wpbc_last_purge_time reported the time of the newest log entry, which could be a deploy. They now report the last successful full purge.
1.0.8
- Fixed: The settings page could open with no data and tabs that did nothing. The page script (assets/admin.js) is served from wp-content, outside /wp-admin/, so Bunny Shield could block or challenge it and Bunny Optimizer could alter it. Two new edge rules turn Optimizer off for the plugin’s own admin files, and turn Shield off for them for logged-in admins only (same secret-cookie protection as the admin and REST rules). Both follow the existing admin switches.
- Improved: Tabs are now real links (?tab=settings and so on). They work and stay on the same tab after a reload even if the page script cannot load, and the Settings form still saves.
- Added: If the page script fails to start, a banner explains why (blocked with HTTP 403, a challenge page instead of JavaScript, or altered on the way) and offers a ”Redeploy edge rules now” button that works without JavaScript.
- Fixed: ”Deploy now” links in the update notices opened the Stats tab instead of Edge Rules.
1.0.7
- Added: Support for WordPress 7.1 client-side media processing (https://make.wordpress.org/core/2026/07/22/client-side-media-processing-in-wordpress-7-1/). The block editor processes images in the browser with WebAssembly, loading about 13 MB of JavaScript from wp-includes/js/dist/script-modules/vips/ and video-conversion/. Bunny Shield could block these files and Bunny Optimizer could try to re-minify them, so image uploads failed unless client-side processing was turned off.
- Added: Edge rule that turns Bunny Optimizer off for the media processing modules, for everyone. They are already minified. Follows the ”Disable Optimizer: admin” switch.
- Added: Role-restricted edge rule that turns Shield off for the media processing modules. Like the admin and REST rules, it requires the secret bypass cookie, so visitors are still inspected. Follows the ”Disable Shield & WAF: admin” switch.
- Note: The upload requests themselves (/wp-json/wp/v2/media/{id}/sideload and /finalize) are covered by the existing REST rule for the roles selected in Settings. If Authors or other roles upload media, add them to the WAF bypass roles.
- Both rules are only deployed on WordPress 7.1 and later.
1.0.6
- Fixed: With Bunny Shield active, the Bricks code element could show ”Could not load code editor”. The editor is a large script loaded from the theme folder that contains PHP keyword lists, which WAF rules can flag. When Bricks is the active theme, the role-restricted Shield bypass (rule 2) now also covers the builder and the theme’s editor assets. It still requires the secret bypass cookie, so visitors are inspected as before.
1.0.5
- Security: The Shield/WAF bypass cookie (wpbc_role) could be forged. Its value was always ”1” and edge rules 2 and 3 only pattern-matched the cookie name, so any request carrying wpbc_role=1 had Shield and the WAF switched off for /wp-admin/* and /wp-json/*. The cookie now carries a per-site secret generated once and stored in a non-autoloaded option, and both edge rules match that exact value.
- Security: Default WAF bypass roles changed from all logged-in users to Administrator + Editor. Sites that explicitly selected roles keep their selection. ”All logged-in users” is still available as an explicit choice.
- Added: ”Rotate bypass secret” button in Settings. Generates a new secret, redeploys edge rules, and re-issues the cookie.
- Added: The bypass cookie is refreshed on admin page loads when it is missing or holds an old secret, so rotating the secret or upgrading does not require admins to log in again.
- Fixed: Third-party cache bypass URLs (wpbc_cache_bypass_urls filter) were deployed as rule 76, after the Cache HTML rule (62). Bunny’s Override Cache Time action is short-circuiting (lowest OrderIndex wins), so those bypasses were ignored and paths such as a custom login URL could be cached for the full TTL. The rule now deploys at OrderIndex 61, before Cache HTML.
- Added: Works with Nahnu Login Shield (https://wordpress.org/plugins/nahnu-login-shield/), our free login security plugin. Login Shield locks out brute-force attackers and can push their IPs to the Bunny.net WAF so they are blocked at the CDN edge. It now appears at the top of the Integrations tab, showing whether it is active, with a one-click install.
- Added: wpbc_bunny_connection filter. Returns api_key, pull_zone_id, shield_zone_id and from_constants so other plugins can reuse the Bunny connection instead of reading settings directly.
- Added: shield_zone_id in the wpbc_status filter output.
- Added: wpbc_deploy_bypass_urls action. Redeploys only the third-party bypass rule(s), a few API calls instead of a full wipe-and-recreate.
- Improved: Edge rules now redeploy automatically the moment the plugin is updated, reinstalled from a zip (same or new version) or activated, with no visitor or WP-Cron needed. The update starts a short background request on the site itself, which loads the new plugin code and deploys the new rules. Previously the deploy ran inside the update request with the old code still loaded, which pushed the old rule set and made remote managers such as MainWP time out and report the update as failed. A WP-Cron fallback runs 60 seconds later if the background request is blocked by the host, and skips itself if the deploy already succeeded.
- Fixed: When a second copy of the plugin was installed in another folder (for example by uploading a zip that WordPress unpacked as nahnu-cache-connector-bunny-net-1.0.5), activating it caused ”constant already defined” warnings and a fatal error. The second copy now stands down and shows an admin notice naming the folder to remove. Deleting a duplicate copy from the Plugins screen no longer erases the settings shared with the copy that stays.
- Fixed: Deploy failed with ”Order index must be unique” for rules split into batches (static asset browser cache, force cache, country lists and similar). Bunny requires a unique OrderIndex for every rule on a pull zone, and all batches of a rule shared one. Every rule now gets its own index, in the intended order, and indices used by rules you created yourself in the Bunny dashboard are left alone.
- Fixed: Settings screen during setup. Test, Refresh (pull zones) and Find zone (DNS, Shield) only used saved settings, so a newly pasted API key reported ”No API key saved” and Shield lookup failed for a pull zone picked but not saved. They now use what is in the form, the key is saved as soon as Bunny accepts it, the pull zone list fills in after a successful Test, and the Shield WAF events section appears on the Stats tab as soon as a Shield zone is found. No page reload needed.
- Fixed: The pull zone name was never saved, so the zone picker could show a blank label after a reload.
- Fixed: Two deploys could overlap (for example the automatic deploy and the admin button) and delete each other’s rules. Deploys are now serialised with a lock.
- Improved: A manual deploy (Deploy / Update buttons, Rotate bypass secret, WP-CLI, REST) always takes priority. If an automatic deploy is running, it stops at its next step and hands over; any automatic deploy still pending (after an update or a plugin activation) sees that a newer deploy already succeeded and skips itself. An automatic deploy that has to wait is retried a minute later instead of being logged as a failure.
- Fixed: Duplicate auto-deploy cron events could be scheduled because the duplicate check never matched.
- Fixed: Every automatic purge hit the Bunny API twice, because wpbc_purge_all had two listeners.
- Improved: Automatic purges (post saves, plugin/theme/core updates, cache plugin clear hooks) are now coalesced into one Bunny API call at the end of the request, after local cache plugins have finished clearing. A single MainWP plugin update could previously trigger 4-6 blocking purges.
- Improved: The cache warmer no longer fetches sitemaps inside the purging request (blocking loopback requests with a 10-second timeout each), and Perma-Cache cleanup no longer calls the Storage API inline. Both now run in WP-Cron. The admin ”Warm now” button, WP-CLI and REST purges still run immediately.
- Fixed: The bypass cookie refresh now also runs on admin-ajax.php requests, so MainWP and similar managers pick up a rotated secret on their next call.
- Added: Hint in the trusted IP whitelist card when MainWP Child is detected, pointing to the dashboard’s outbound IP.
- Fixed: Background deploys (cron, auto-deploy, wpbc_deploy, WP-CLI, REST) read the cache TTL from the wrong option and reset rule 62 to 7 days, ignoring the TTL saved in the Edge Rules tab.
- Fixed: When specific rules were selected in the Edge Rules tab, batched rules (any pattern list over 5 entries) only deployed their first batch.
- Added: wpbc_mark_rules_stale action. Flags rules as out of date; the 5-minute cron check redeploys and admins see a pending notice with a Deploy now button.
1.0.4
- Added: xSpeed Cache — cache purge sync via xspeed_after_purge_all (full purge).
1.0.3
- Added: Auto-deploy edge rules when the plugin updates or a supported plugin is activated/deactivated. Runs in the background via WP-Cron 30 seconds after the trigger. Result logged to the Purge Log.
- Added: WP-CLI commands — wp bunny deploy, wp bunny purge, wp bunny status, wp bunny rules.
- Added: Admin notice when a supported plugin is activated or deactivated confirming background rule update. Persists until the deploy completes or the admin dismisses it.
- Added: Public PHP API (filters and actions) for third-party plugin integration — wpbc_is_connected, wpbc_status, wpbc_last_purge_time, wpbc_purge_all, wpbc_purge_url, wpbc_deploy, wpbc_update_rules.
- Added: REST API endpoints under /wp-json/wpbc/v1/ — GET /status, POST /purge, POST /purge-url, POST /deploy. Authenticated via X-WPBC-Token header or WordPress admin session.
- Added: REST API token field in Settings with copy and regenerate buttons.
- Added: API documentation tab in the plugin admin showing all REST endpoints, PHP filters, PHP actions, and integration filters with copy-paste code examples.
1.0.2
- Fixed: Stable tag corrected to 1.0.2 to resolve WordPress.org serving incorrect version.
1.0.1
- Added: Vary Cache by Accept-Language — automatically configured on the pull zone when WPML, Polylang, or TranslatePress is active.
- Added: Shield WAF event log panel on the Stats tab — view blocked IPs, triggered rules, and URLs for the last 1, 6, 24, or 72 hours.
- Added: Shield Zone ID field in Settings.
- Added: Request Coalescing toggle in Settings.
- Added: Admin notice after plugin updates prompting a redeploy of edge rules.
- Updated: Tested up to WordPress 7.1.
1.0.0.5
- Added: wpbc_shield_bypass_ips filter — third-party plugins can add trusted IPs/CIDRs to the Bunny Shield WAF bypass list (rule 74) without any code changes to this plugin.
- Added: wpbc_shield_bypass_urls filter — third-party plugins can disable Shield WAF on specific URL path patterns (rule 75, new).
- Added: wpbc_cache_bypass_urls filter — third-party plugins can add URL paths to the Bunny cache bypass list (rule 76, new).
- Added: wpbc_compatible_plugins filter — third-party plugins can register themselves in the Integrations tab.
1.0.0.4
- Fixed: Plugin settings (API key, pull zone) could be wiped during plugin updates, option imports, or multisite sync. Added a sanitize guard that aborts if the incoming data has no recognisable form submission markers, and a pre_update_option filter as a second line of defence.
1.0.0.3
- Fixed: Bunny edge cache now always purges when a cache plugin is updated, regardless of the ”Plugin/theme updates” trigger setting. Previously the purge was skipped if that toggle was off.
1.0.0.2
- Added: BerqWP integration — berqwp_flush_all_cache and berqwp_purge_cdn (full purge), berqwp_flush_page_cache (per-URL path slug).
1.0.0.1
- Added: SWIS Performance by EWWW Image Optimizer integration — swis_complete_cache_cleared and swis_site_cache_cleared (full purge), swis_cache_by_url_cleared (per-URL).
- Updated: Tested up to WordPress 7.0.1.
1.0.0.0
- Initial public release.